Do you know how your team responds to a real phishing email?
ReefSecure Angler tests exactly that, safely. We design and run realistic phishing campaigns for your organisation, measure what happens and give you a report you can act on.
- Pluritech, Vilvoorde, since 1994
- GDPR compliant, EU data
- We set everything up for you
Attacks target people, not systems
Phishing emails imitate legitimate messages: a supplier, a delivery service, a government agency. One click on the wrong link can open the door to a data breach, a locked system or financial fraud. No technical measure catches all of it.
That is why we test it. Not to catch employees out, but to let them experience a realistic situation and then show them what should have given it away: the suspicious link, the sender address that is slightly off, the tone that pushes a little too hard.
How a campaign runs
Every campaign is bespoke. Copy and storylines are written by people, tuned to your business context and often based on a current news event.
Scoping
A session with those responsible. We set the scope, the ground rules, the KPIs and the exclusions, and obtain formal approval.
Simulation
A scenario tailored to your context, sent within the agreed frame, with every interaction measured safely.
Kill switch
If the bait works too well and starts disrupting operations, we stop the campaign immediately and neutralise its effect.
Report
An executive and a technical report, a heatmap per department and a session in which we walk through the conclusions.
Thirteen attack methods, one platform
Across the year we deliberately alternate, so that employees do not learn to watch for a single pattern.
Password reset phishing
A fake password reset email with a matching form. The classic, and in practice the one that works most often.
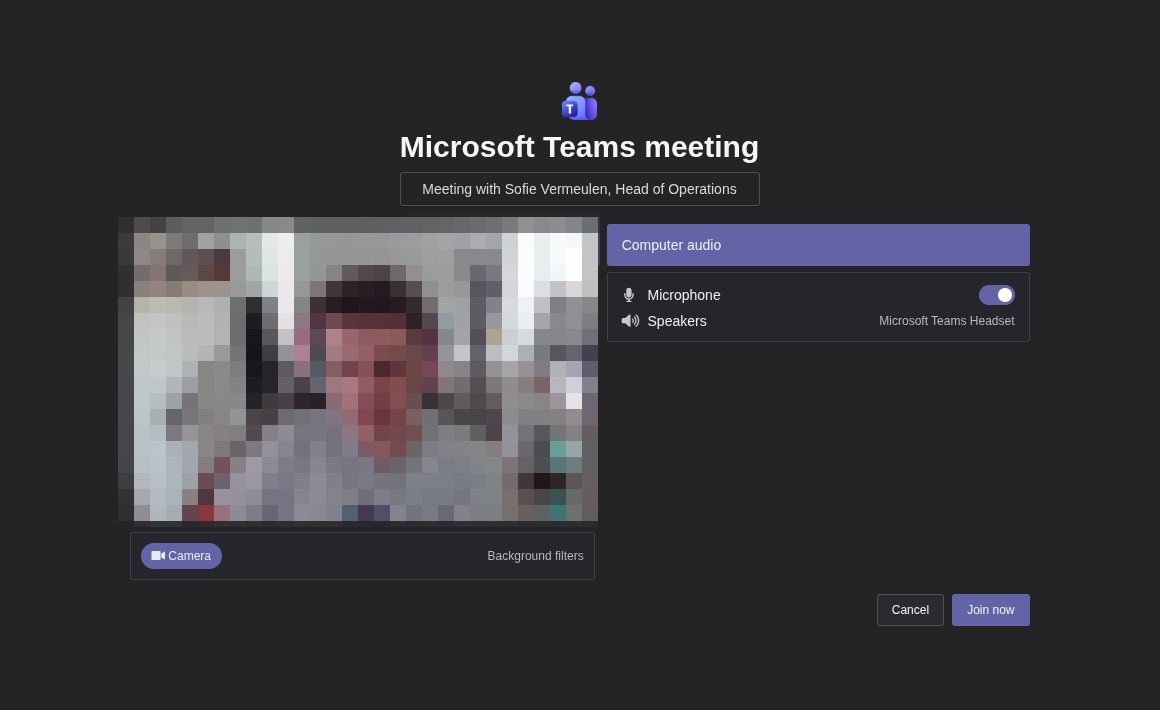
Meeting phishing
A replica Teams or Zoom screen. Records clicks, camera and microphone permissions and join attempts.
Business Email Compromise
CEO fraud. An email thread on behalf of management or finance asking for a payment or a changed IBAN.
Fake invoice
An invoice that appears to come from a supplier, with an altered account number or a payment reminder.
QR code phishing
An email with a QR code. Tracks the scan and the browser and device used to open it.
Vishing
A phone simulation on behalf of IT or finance. Measures how many people call back and whether they give up a PIN or password.
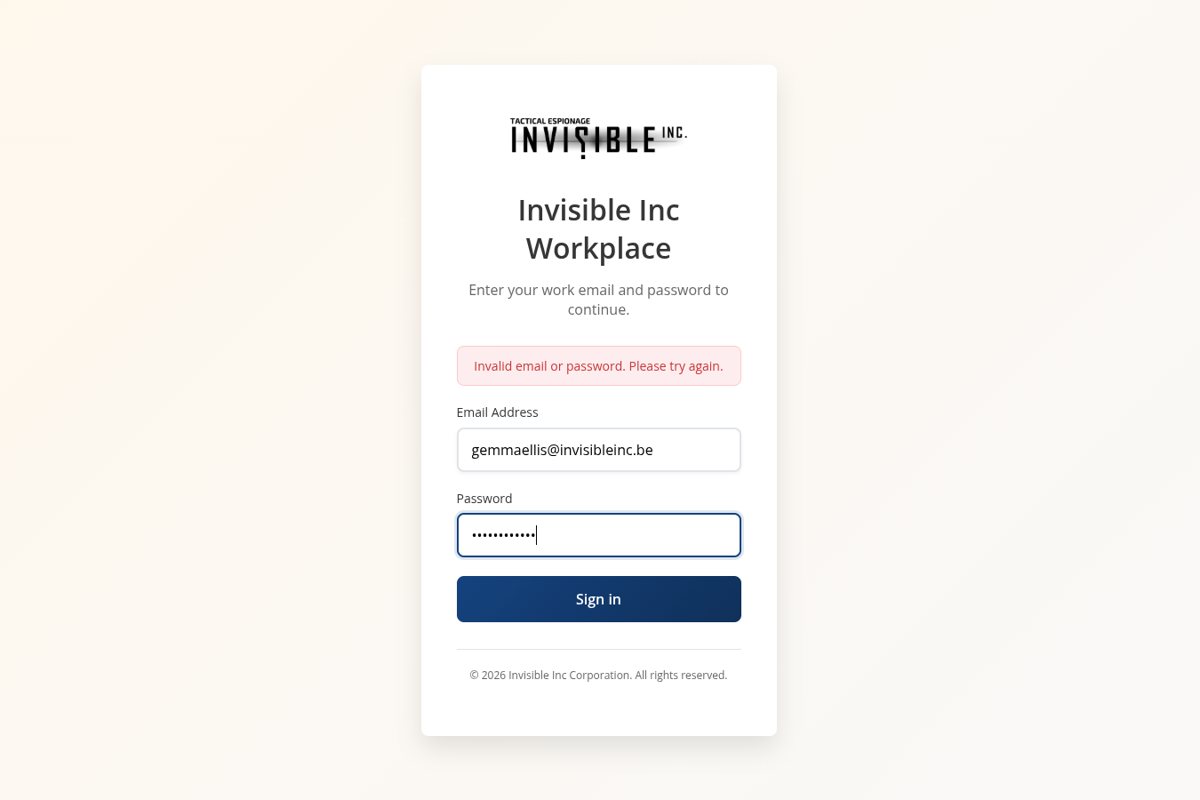
- Employee portal scam
- Malicious attachment
- Callback phishing
- Smishing
- Social media impersonation
- USB drop
- AI-written personal emails
A report that cleans the numbers first
Mail filters such as Microsoft Defender Safe Links, Mimecast and Proofpoint open every link automatically, within seconds of sending. Counting those hits gives a click rate that means nothing. We filter that out: only genuine browser sessions are scored.
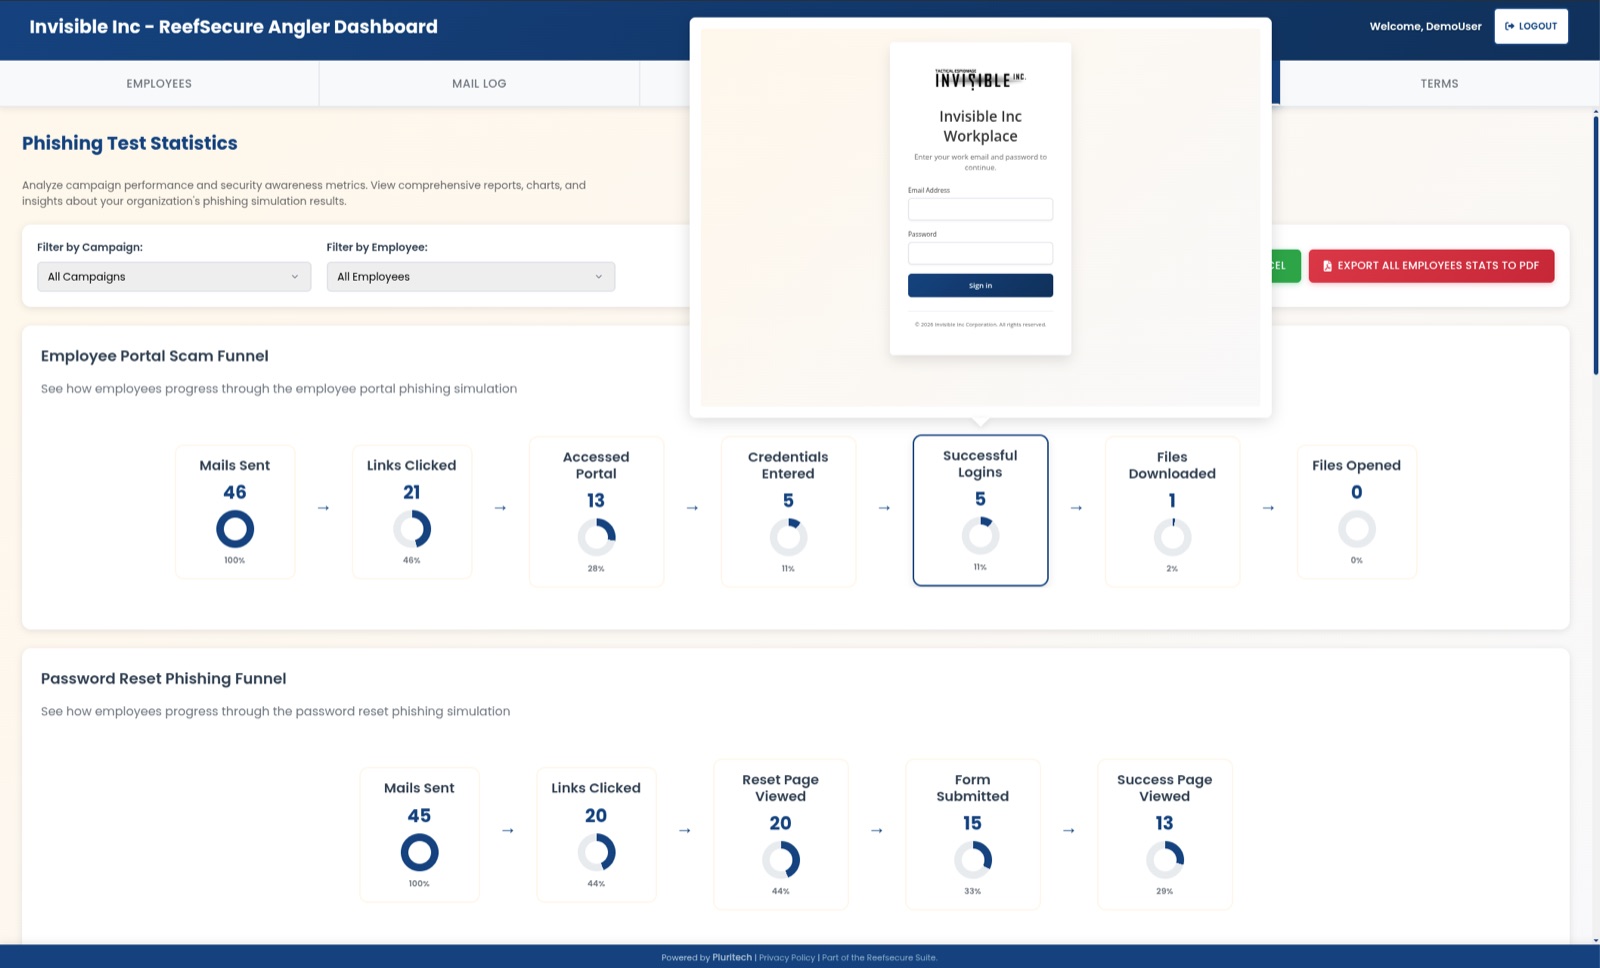
- The funnel per method and per department, scanners excluded
- A heatmap per department and per risk profile
- Concrete recommendations: process, training, technology
- Export to PDF for management, to Excel for your own analysis
- Fully anonymised reporting on request
- A closing session on site or via Teams
Is your data at risk during the exercise? No.
A phishing simulation only makes sense if it is safer than the attack it imitates. The platform is built so that there is nothing to steal, not even by us.
- Passwords entered are not stored. Only the fact that something was entered is recorded.
- The replica pages collect no company data.
- GDPR compliant, with a data processing agreement.
- Scope, exclusions and KPIs are agreed in writing before a single email goes out.
- You supply the address list and thereby set the scope.
Book a 20-minute demo
We show you the environment, walk through a sample report and discuss which scenario is most realistic for your organisation. Only then do you decide.
Prefer to talk now? Call +32 2 270 01 32 or email sales@pluritech.com.
Thank you, we have your request
We will contact you to plan the demo. Prefer to talk now? Call +32 2 270 01 32.